The AI Toolkit for TypeScript. From the creators of Next.js, the AI SDK is a free open-source library for building AI-powered applications and agents
My analysis
Inside the Vercel AI SDK Tool Loop
How the AI SDK separates provider adapters, typed tools, generation steps and UI streams, and where production applications need stronger boundaries.
TN
TIAN NEWS AI
Published · Updated · 4 min read
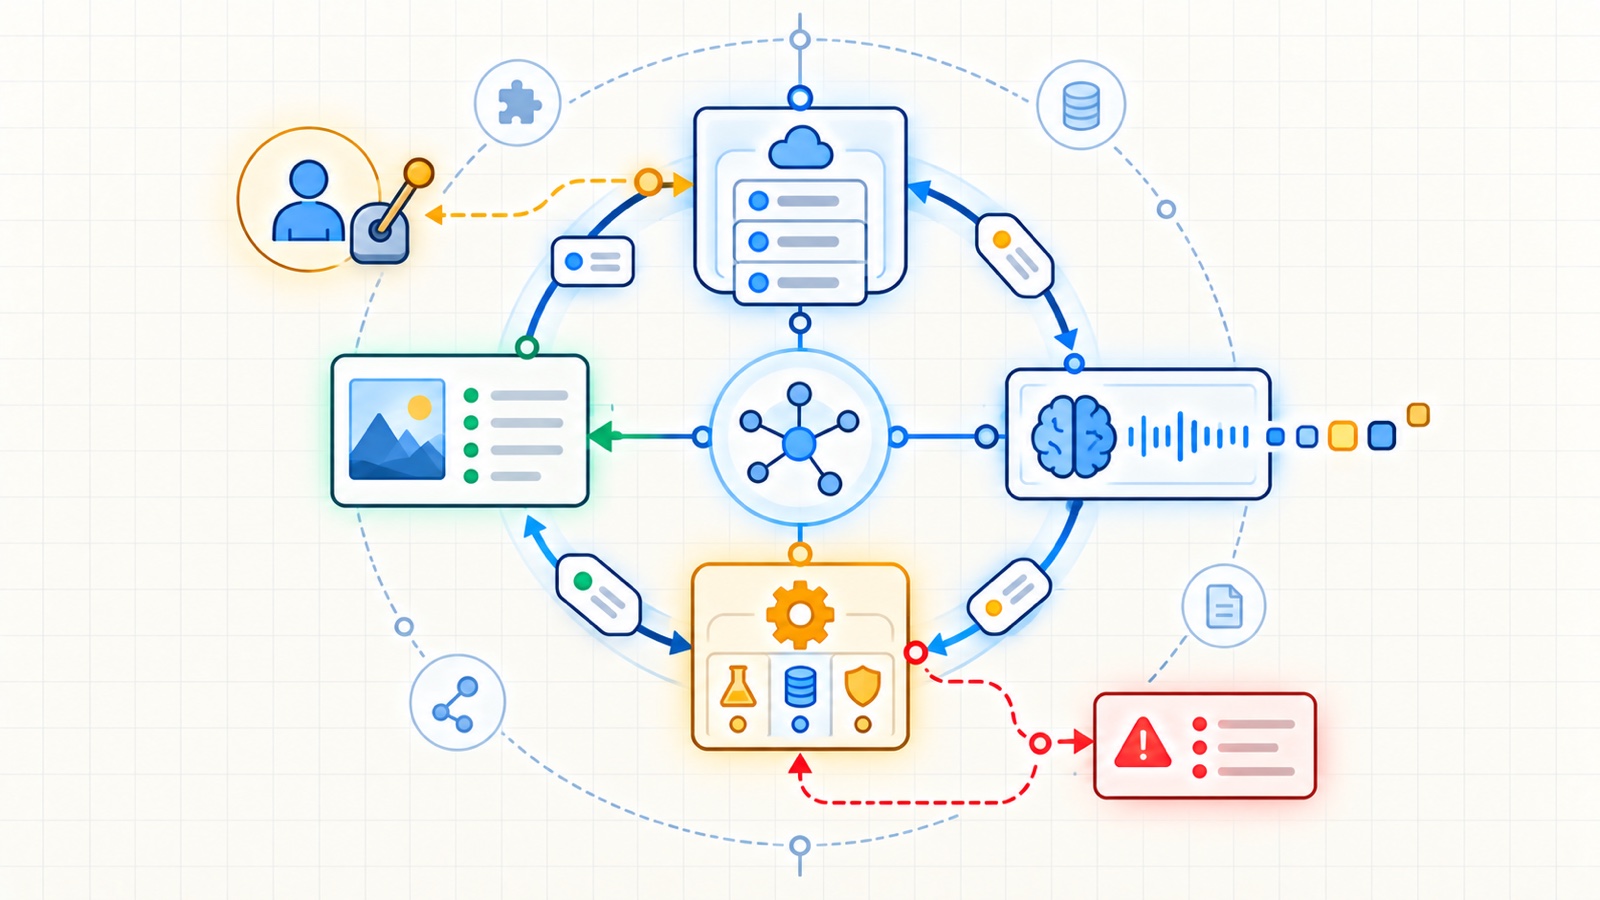
The Vercel AI SDK is often introduced through a short streamText example. The more durable idea sits underneath: application code talks to a shared language-model interface, provider packages translate that interface and tool calls become typed events inside a multi-step generation loop.
That architecture reduces provider-specific code. It does not remove the need for authorization, idempotency or durable state.
Updated
Describes the AI SDK Core and repository architecture documented on October 2, 2026. APIs are versioned and evolve quickly; pin the installed major version and consult its migration guide.
The repository separates the main ai package from provider specifications, shared provider utilities and concrete provider adapters. Application code can call a common generation API while an adapter translates request and response details for a selected model service.
Conceptually:
text
application
    -> ai: generateText / streamText
        -> provider specification
            -> provider adapter
                -> external model API
This boundary makes model switching possible, but not automatically safe. Models differ in tool-schema support, streaming events, usage metadata and error behavior. Test the providers and models you deploy instead of assuming the common type erases those differences.
A tool is a contract plus an optional executor
An AI SDK Core tool has a description, an input schema and optionally an execute function. The schema constrains the data passed from the model and provides TypeScript inference to the handler.
weather.ts, ts
const weather = tool({ description: "Read the current weather for one supported city", inputSchema: z.object({ city: z.enum(["hanoi", "danang"]) }), execute: async ({ city }) => weatherService.read(city),});
Schema validation answers “Is this input shaped correctly?” It does not answer “May this user perform this operation?” Authorization belongs inside or immediately before the application service that owns the effect.
Key takeaway
Treat tool descriptions as model guidance and tool handlers as security boundaries. The model may choose a tool, but trusted code must validate identity, scope, arguments and current state before any side effect.
One generation is not automatically a loop
With generateText or streamText, a model can return a tool call as the result of a step. A multi-step workflow feeds tool results back into another generation until a stop condition is reached.
The SDK exposes step data so the application can inspect intermediate calls and results. A stop condition such as a maximum step count is essential. “Continue until the model is done” is not an operational budget.
text
messages -> model step -> tool call -> validated execution
    ^                                      |
    |----------- tool result --------------|
Production limits should include total steps, tool calls, model usage, elapsed time and external-service cost.
Streaming is an event protocol
streamText yields more than text fragments. A stream can carry reasoning parts, tool-call starts and deltas, completed tool calls, tool results, sources, files, usage and errors.
The UI should render from typed events rather than parse human-readable text. It also needs an explicit persistence boundary. A browser disconnect must not leave the server uncertain about whether a consequential tool completed.
Persist authoritative conversation and tool outcomes server-side. Reconnect the UI to that state rather than treating the current React component tree as the record.
Approval is a separate round trip
The SDK supports tools that require approval. The first model call produces an approval request; the application collects a decision and supplies an approval response in a later call.
The application must bind that approval to the exact tool name, arguments, user and expiration. If any relevant input changes, ask again. Do not reuse a generic “approved” flag for a modified payment, command or destination.
Error handling belongs at every boundary
Separate failures into:
invalid model-generated tool input;
unknown or unavailable tool;
rejected approval;
handler error;
provider rate limit or timeout;
stream interruption;
successful side effect followed by lost response.
The last case requires idempotency. Retrying a model step without knowing whether a tool completed can duplicate the effect.
Define provider-independent application operations before exposing tools.
Give each tool a narrow schema and explicit authorization check.
Set stop conditions and budgets for every multi-step call.
Record step, tool-call and tool-result identifiers server-side.
Require bound approval for consequential operations.
Make side-effecting handlers idempotent and observable.
Test provider differences, disconnects and retries before adding UI polish.
What to borrow from the repository
The provider boundary is a useful pattern beyond LLMs: keep application code dependent on a capability contract and isolate vendor translation. The typed tool contract is also valuable when the executor is a queue or remote service rather than an inline function.
What not to infer is equally important. A shared SDK cannot decide your data-retention policy, transaction boundary or threat model. Those responsibilities stay in the application around the tool loop.